An unprecedented series of reported cyberattacks and security threats has raised serious concerns across Europe, with incidents affecting everyday life, economic activity, healthcare services and air travel within just a few days.
Hackers reportedly managed to interfere with supermarket refrigeration systems in several European countries, raising temperatures to as high as 50 degrees Celsius and destroying large quantities of food. In France, a similar incident affected blood storage facilities, while a French bank reported losses of approximately €100 million following a cyberattack.
During the same period, the international cryptocurrency market was shaken by reports of a $6.4 billion theft from Binance, while European airlines faced successive bomb threats targeting passenger aircraft.
These developments have heightened concerns about the security of internet-connected systems used in critical economic and social infrastructure.
They have also renewed discussion about the possibility of hybrid destabilisation operations, although there is currently no evidence that the different incidents form part of a coordinated campaign.
Supermarket refrigeration systems targeted as temperatures reach 50°C
One of the most unusual aspects of the reported wave of cyberattacks involves refrigeration and freezer systems operated by major retail chains.
On 2 November, businesses in at least seven European countries reported problems with their refrigeration facilities, resulting in food spoilage and the withdrawal of products from sale.
In Belgium, stores belonging to chains including Carrefour, Delhaize, Intermarché and Spar were affected. Similar problems were reported in Sweden, Ireland, the Netherlands, Luxembourg, Finland and Estonia.
In Sweden, ICA and Coop stores experienced sudden increases in refrigeration temperatures. At one ICA supermarket, the temperature reportedly reached 50°C, destroying stored products.
In Ireland, Musgrave announced that refrigeration systems at 13 SuperValu stores had been affected. Refrigerated and frozen products were withdrawn from sale as a precaution.
Similar interference was identified at facilities in Belgium, where technicians were forced to disconnect equipment from networks to limit the damage.
The incident was not isolated. In October, hackers reportedly interfered with refrigeration systems at hundreds of French supermarkets, causing substantial financial losses and, according to reports, even fires.
The European Commission expressed concern about the repeated attacks, with Agriculture and Food Commissioner Christophe Hansen treating them as a threat to food supply chains and consumer confidence.
How could hackers manipulate refrigeration temperatures?
What makes these attacks particularly concerning is that they were not limited to electronic files or databases. They reportedly affected the operation of physical equipment.
Modern commercial refrigeration units are equipped with monitoring and remote management systems. These allow technicians to check temperatures, identify faults and adjust operating settings without being physically present at the premises.
However, the same technology can create vulnerabilities when insufficiently protected.
Cybersecurity researchers warn that internet-accessible industrial control devices can become targets, particularly when they use outdated software or inadequately secured access accounts.
Authorities have not released a definitive technical assessment explaining how the attackers gained access to the systems involved.
France: Blood storage facilities targeted
Even greater concern has emerged over incidents affecting facilities directly connected to public healthcare.
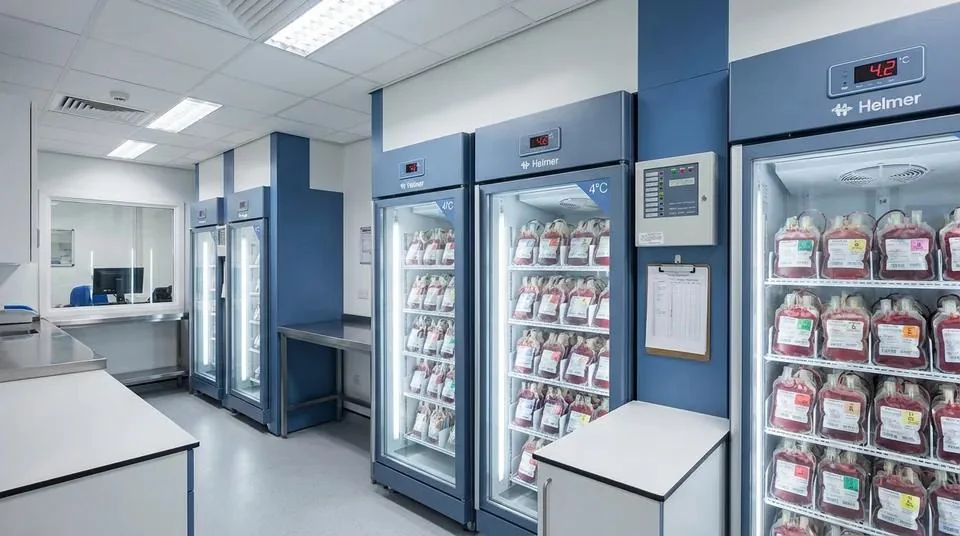
In early November, three regional facilities operated by the French Blood Establishment, Établissement Français du Sang (EFS), were reportedly affected by a cyberattack targeting refrigeration monitoring and control systems.
The incident occurred overnight between 1 and 2 November, around the same time as the reported attacks on European supermarkets.
Staff were alerted by alarm systems and transferred blood supplies to alternative refrigeration units that were not connected to the affected network.
The French Ministry of Health announced that the situation had been brought under control and that remote access to the affected equipment had been disabled.
According to EFS, blood supplies were not affected.
The incident highlights a critical aspect of cybersecurity: digital interference can threaten equipment essential to medical services, even without compromising patients’ electronic medical records.
French bank loses approximately €100 million in cyberattack
In the financial sector, French banking group Crédit Mutuel Arkéa announced that cybercriminals had stolen approximately €100 million through unauthorised transactions.
The incident became public on 4 November, with further details confirmed on 5 November.
According to the bank, the perpetrators used an account belonging to the financial institution to carry out fraudulent money transfers.
Management announced that efforts were underway to recover the funds and that customers’ assets had not been affected.
Certain transactions were temporarily suspended as a precaution, resulting in delays to money transfers.
French prosecutors are investigating the case. The identities of those responsible have not been definitively established.
Binance: Multibillion-dollar theft and suspicions involving North Korea
On 29 October, international cryptocurrency exchange Binance was reportedly targeted in one of the largest recorded thefts of digital assets.
According to blockchain analytics company Chainalysis, attackers stole approximately $6.4 billion from the platform’s digital wallets, transferring funds across different blockchain networks.
Based on its analysis, Chainalysis linked the attack to TraderTraitor, a group believed to have connections to North Korea.
Some of the stolen assets were converted into different cryptocurrencies, while asset-freezing procedures were initiated.
Approximately $2.8 billion had reportedly been frozen, according to Chainalysis’s initial assessment.
The incident illustrates the potential scale of digital financial attacks and the difficulties involved in tracing and recovering funds transferred rapidly through international networks.
Although the reported attack was not directed exclusively at Europe, it carries particular significance for the European cryptocurrency market, where millions of investors and businesses operate.
European flights face bomb threats, diversions and fighter jet escorts
As European authorities respond to cyberattacks, a separate but equally concerning series of incidents has placed aviation security services on heightened alert.
Since 3 November, European airlines have reportedly received successive bomb threats targeting passenger aircraft, resulting in emergency landings, flight diversions and intensified security inspections.
Airlines affected include Ryanair, Wizz Air, Finnair, Aer Lingus, LOT Polish Airlines, easyJet and Aegean Airlines.
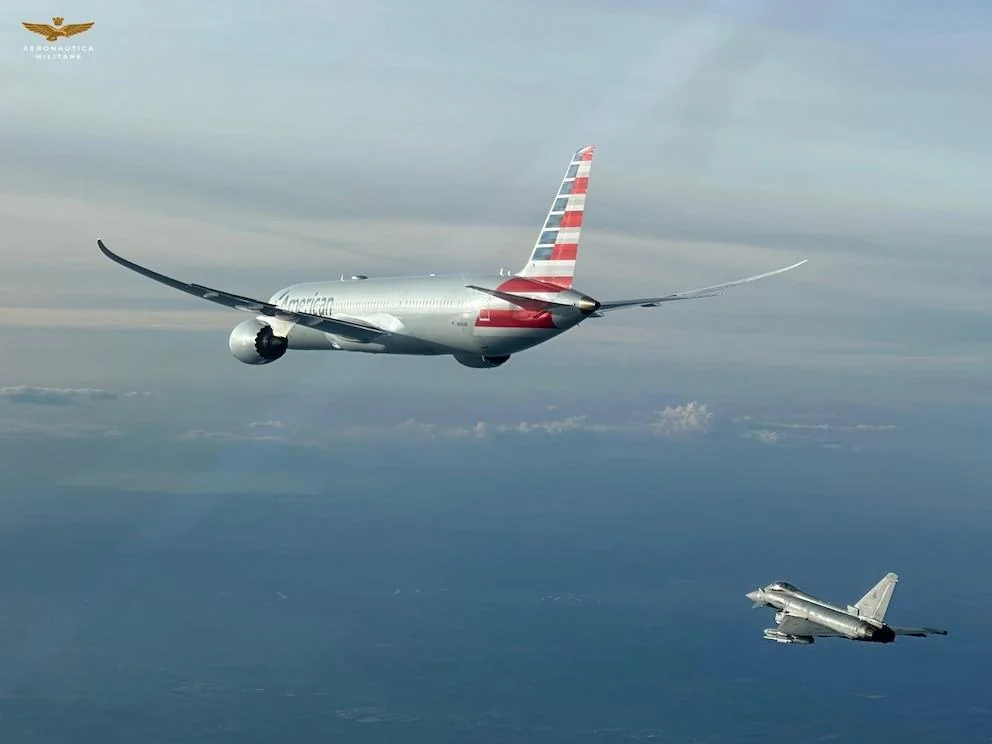
According to reports, approximately 20 flights were affected, with military aircraft deployed in some cases to escort passenger planes.
Security searches did not uncover actual explosive devices. Nevertheless, authorities emphasise that every such threat must be treated as potentially genuine until investigations are completed.
Aer Lingus flight diverted to French military airbase
One of the most serious incidents involved an Aer Lingus flight travelling from Dublin to Rome.
The aircraft, carrying 151 passengers and six crew members, was diverted to the Évreux-Fauville military airbase in Normandy, France, following a bomb threat.
According to reports, French fighter jets were deployed to escort the aircraft.
After landing, military personnel and explosive ordnance disposal specialists conducted security checks.
The aircraft landed safely, and no explosives were discovered.
Finnair flights targeted by threats
A similar security operation involved a Finnair flight travelling from Helsinki to Rome.
The aircraft was escorted by Italian military jets following a warning about a possible bomb.
It landed safely at Rome’s Fiumicino Airport, where the necessary security inspections were carried out.
A second Finnair flight, bound for Vienna, also received a threat but continued its journey and landed without incident.
Both threats proved unfounded.
Ryanair and Wizz Air flights affected across Europe
Ryanair flights bound for Sofia from several European airports, including London, Madrid and Copenhagen, were also reportedly targeted.
In one case, an aircraft departing from London Stansted was diverted to Plovdiv, Bulgaria.
Meanwhile, a Wizz Air flight travelling from Milan to Warsaw was diverted to Vienna.
Additional security inspections were conducted in Prague, where four arriving flights were affected by warnings about possible explosive devices.
Bomb threat reported on Prague–Larnaca flight
On 6 November 2026, four flights arriving at Prague Airport and five departing flights were targeted by new bomb threats, airport spokesperson Denisa Hejtmánková told Agence France-Presse (AFP).
“The threats concern arrivals from Denmark, the United Kingdom and two from Spain. As for departures, these involve flights to the Netherlands, Cyprus, Romania, Italy and the United Kingdom,” she said.
However, the flight bound for Larnaca, which had been mentioned in connection with a bomb threat, landed normally and safely at Larnaca Airport, reliable sources told the Cyprus News Agency (CNA).
Who is behind the bomb threats?
Authorities are investigating whether the threats originated from individual perpetrators or formed part of an organised attempt to disrupt European air transport.
According to Reuters, the threats have frequently been communicated through anonymous emails or telephone calls.
British authorities described some incidents as malicious hoaxes, while security experts noted that the concentration of so many threats within a short period was unusual.
There has been no publicly confirmed identification of the perpetrators or official attribution to a particular state or organisation.
Even when threats prove false, they can generate substantial financial costs, cancellations, delays, passenger disruption and the mobilisation of significant police and military resources.
Aviation cybersecurity concerns: The Amadeus vulnerability
The wave of bomb threats coincides with increased attention to digital security within the aviation industry.
Spanish travel technology company Amadeus announced in October that it had identified a vulnerability affecting an environment used to display booking information.
According to its official statement, certain booking data could be accessed through the vulnerability.
The company said there was no evidence that payment details or other financial information had been accessed, nor any indication that the vulnerability had been exploited in a ransomware attack.
Amadeus announced that it had implemented corrective measures and strengthened its systems monitoring.
This incident is separate from the bomb threats. Nevertheless, it demonstrates the importance of protecting the digital infrastructure supporting international aviation.
There is no evidence linking the Amadeus vulnerability to the threats against passenger flights.
United Kingdom: Ransomware attack on school network raises AI concerns
On 3 November, technical findings were published concerning a ransomware attack on a school network in the United Kingdom.
The attackers reportedly managed to encrypt 37 of approximately 50 systems they had accessed.
The attack took place in September, although the technical findings were released in early November.
According to cybersecurity company Bitdefender, the perpetrators used tools to steal credentials, explore the network and extend their access to additional systems.
Researchers identified indications suggesting that artificial intelligence may have been used to assist the attack.
However, they could not confirm whether a particular AI model or automated system had been involved.
The case adds to concerns about the growing sophistication of cyberattacks and the potential use of emerging technologies by cybercriminals.
Europe faces growing security challenges
The incidents highlight the vulnerability of interconnected systems supporting essential services, from food distribution and healthcare to financial transactions and aviation.
They also demonstrate how security threats can disrupt everyday activities even when no physical attack ultimately takes place.
Although the concentration of incidents has prompted discussion about possible coordinated or hybrid operations, no publicly confirmed evidence establishes a connection between the various cases.
The challenge for European authorities is to strengthen resilience, investigate the individual incidents and protect critical infrastructure without drawing premature conclusions about who may be responsible.